Most reservation fraud is preventable: insist on platform payments, lock down platform accounts, and verify any unexpected payment requests by phone. The Digital Services Act gives EU platforms a formal duty to act on fraud reports, national CERTs like Germany's BSI track live campaigns, and tools such as Served help venues keep bookings on trusted channels in the first place.
TL;DR:
- Enforcing multi-factor authentication and regular audits significantly reduce the risk of platform account hijacking for hotels and travel businesses.
- Always verify booking links, compare reservation details, and avoid paying through unsolicited email links to detect most reservation scams before money is lost.
- Only complete payments on official platforms, and independently call the venue to verify any unusual or urgent payment requests.
- Reporting suspected fraud swiftly to banks, platforms, and authorities is crucial; preserve evidence like email headers and transaction references for investigation.
- Using a trusted, centralized booking channel like Served limits off-platform communication and reduces guest exposure to phishing campaigns.
Table of Contents
- How reservation scams and account hijacking actually work
- Red flags that reveal a scam before you lose money
- Prevention for hotels and travel businesses
- Prevention for travellers and corporate bookers
- Responding to suspected fraud: an ordered checklist
- What the evidence shows about account compromise and platform duty
- Priority actions for teams with limited resources
- A practical way to keep bookings on a trusted channel
- FAQ
- Sources
How reservation scams and account hijacking actually work
Reservation fraud rarely starts with a dramatic hack. It usually starts with a convincing message that looks like it came from a platform you already trust. Attackers clone booking confirmation pages, harvest card details, then vanish before anyone notices.
Account takeover is the more damaging variant. Once a criminal controls a hotel's or host's platform login, they can message real guests with payment requests that look entirely legitimate, because they are sent from a genuine, verified account.
- Phishing emails and cloned booking pages designed to harvest payment details
- Account takeover of hotel or host platform logins, used to send convincing follow-up payment demands
- Reuse of real booking details (name, dates, reference number) to craft personalised spear-phishing
- Fake listings and social media offers that redirect guests to fraudulent payment pages
Security researchers have documented phishing campaigns that repurpose genuine hotel reservation data, pulled from hundreds of properties, to make follow-up scam messages far harder to spot.
Red flags that reveal a scam before you lose money
Most reservation scams share tells, once you know where to look. Train yourself and your staff to run through these checks before clicking a link or re-entering card details.
- Inspect the sender address and the URL character by character, watching for subdomain tricks and swapped letters.
- Never re-enter payment details on a site reached through an unsolicited link; type the platform's address manually instead.
- Compare the booking reference, PIN and confirmation details against what the platform itself shows you.
- Treat any unexpected change to payment terms, especially a switch to bank transfer, as a serious warning sign.
- Be wary of urgent, pressure-based language demanding immediate action.
Pro Tip: If a message asks you to "confirm payment urgently" outside the platform, assume it is fraudulent until you have verified it independently by phone.
Prevention for hotels and travel businesses
Technical discipline stops most reservation fraud before it reaches a guest. The strongest venues treat their booking systems the way they treat a till: access is limited, logged and checked daily.
Start with identity controls. Every staff account on a channel manager or property management system should require multi-factor authentication, and access should be scoped to what each role actually needs. A front-desk login has no business touching payment settings.
Third-party integrations deserve the same scrutiny. Many breaches trace back to an old API key or a plugin nobody remembers connecting. Audit integrations regularly, and revoke any credential that is not actively in use.
- Enforce MFA and least-privilege access on every PMS and channel manager account
- Audit third-party integrations and API keys, and revoke unused credentials
- Route payments through the platform itself, or use virtual, one-time corporate cards to limit exposure
- Set alerts for bulk booking edits, payment-method changes and unusual check-in patterns
- Run regular phishing training with a documented escalation path for staff who spot something odd
National advisories have tracked large-scale campaigns exploiting exactly these gaps. BSI reported thousands of fake booking domains circulating in a single campaign, built to collect guest payment information through confirmation emails the guest never requested.
Pro Tip: A daily five-minute review of flagged account activity catches most takeover attempts before a fraudulent message ever reaches a guest.
Listing quality matters too. A property page built from dark, cluttered or mismatched photos is easier for a scammer to clone convincingly, because guests already expect an unpolished page. Services like Hospitality Lens help operators keep listing images consistent and professional, which makes a cloned or copied page far easier for guests to spot as fake.

Prevention for travellers and corporate bookers
Travellers and corporate travel teams carry their own half of the responsibility. The habits below take seconds and close off the most common attack paths.
- Complete every payment through the booking platform, or use a centralised corporate virtual card rather than sharing a personal one
- Call the hotel using the number listed on the official booking confirmation, never a number from an unsolicited message
- Keep payment receipts, confirmation PINs and transaction IDs, and reconcile them against your statement immediately
- Avoid clicking links from unknown senders, and forward anything suspicious to the platform for verification
Consumer protection guidance is consistent on this point: complete payments only on the platform itself, and verify any unusual payment request by phone before acting on it. If you are booking ground transport as part of a trip, the same logic applies: verify the provider's credentials rather than trusting a message that lands in your inbox, using a resource such as Ride Scouts' verification checklist as a model for what to check.
Responding to suspected fraud: an ordered checklist
Speed matters once fraud is suspected. Work through these steps in order, without waiting to see if the situation resolves itself.
- Contact your bank or card issuer immediately to freeze the card or dispute the charge.
- Report the incident to the booking platform through its official reporting mechanism.
- Preserve evidence: screenshots, email headers, transaction references and timestamps, before anything gets deleted.
- If you are in the EU, use the platform's DSA notice-and-action mechanism and notify your national consumer protection body or police where relevant.
If your confirmation has simply gone missing rather than being clearly fraudulent, check the practical steps in this guide to tracking down a missing booking confirmation before escalating.
What the evidence shows about account compromise and platform duty
The DSA requires platforms to give users a straightforward way to report fraudulent listings and to act on well-documented reports promptly, which puts formal pressure on large platforms to close fraudulent listings quickly rather than leaving them live for weeks. Account compromise remains the vector worth worrying about most, because a takeover lets an attacker send messages from a genuinely verified identity.
- MFA and daily activity monitoring directly address the account takeover vector that enables convincing follow-up fraud
- Platforms have reset guest PINs after data incidents, specifically to blunt follow-up phishing attempts
- A commission-free, centralised booking page with human support keeps guests on one trusted channel instead of scattering communication across email, social media and third-party messages
Priority actions for teams with limited resources
If you can only do three things this month, do these: enforce MFA everywhere, block off-platform payment requests outright, and add a phone-verification step for any high-value booking. Everything else, including automated anomaly detection and tighter integration governance, can follow once those basics are solid.
Measure success honestly. The number that matters is not how many alerts your system generates, it is how many off-channel payment requests your guests actually report to you, and how that number falls over time.
— Ignacy Jurkowski
A practical way to keep bookings on a trusted channel
Reservation fraud thrives on fragmented communication: guests messaging through email, social media and third-party chats, each one a potential opening. We built Served around the opposite idea. Every booking runs through one commission-free, flat-subscription platform, with no per-cover fees and no reselling of guest data, reducing the risk of off-platform payment links that guests might be tricked by.
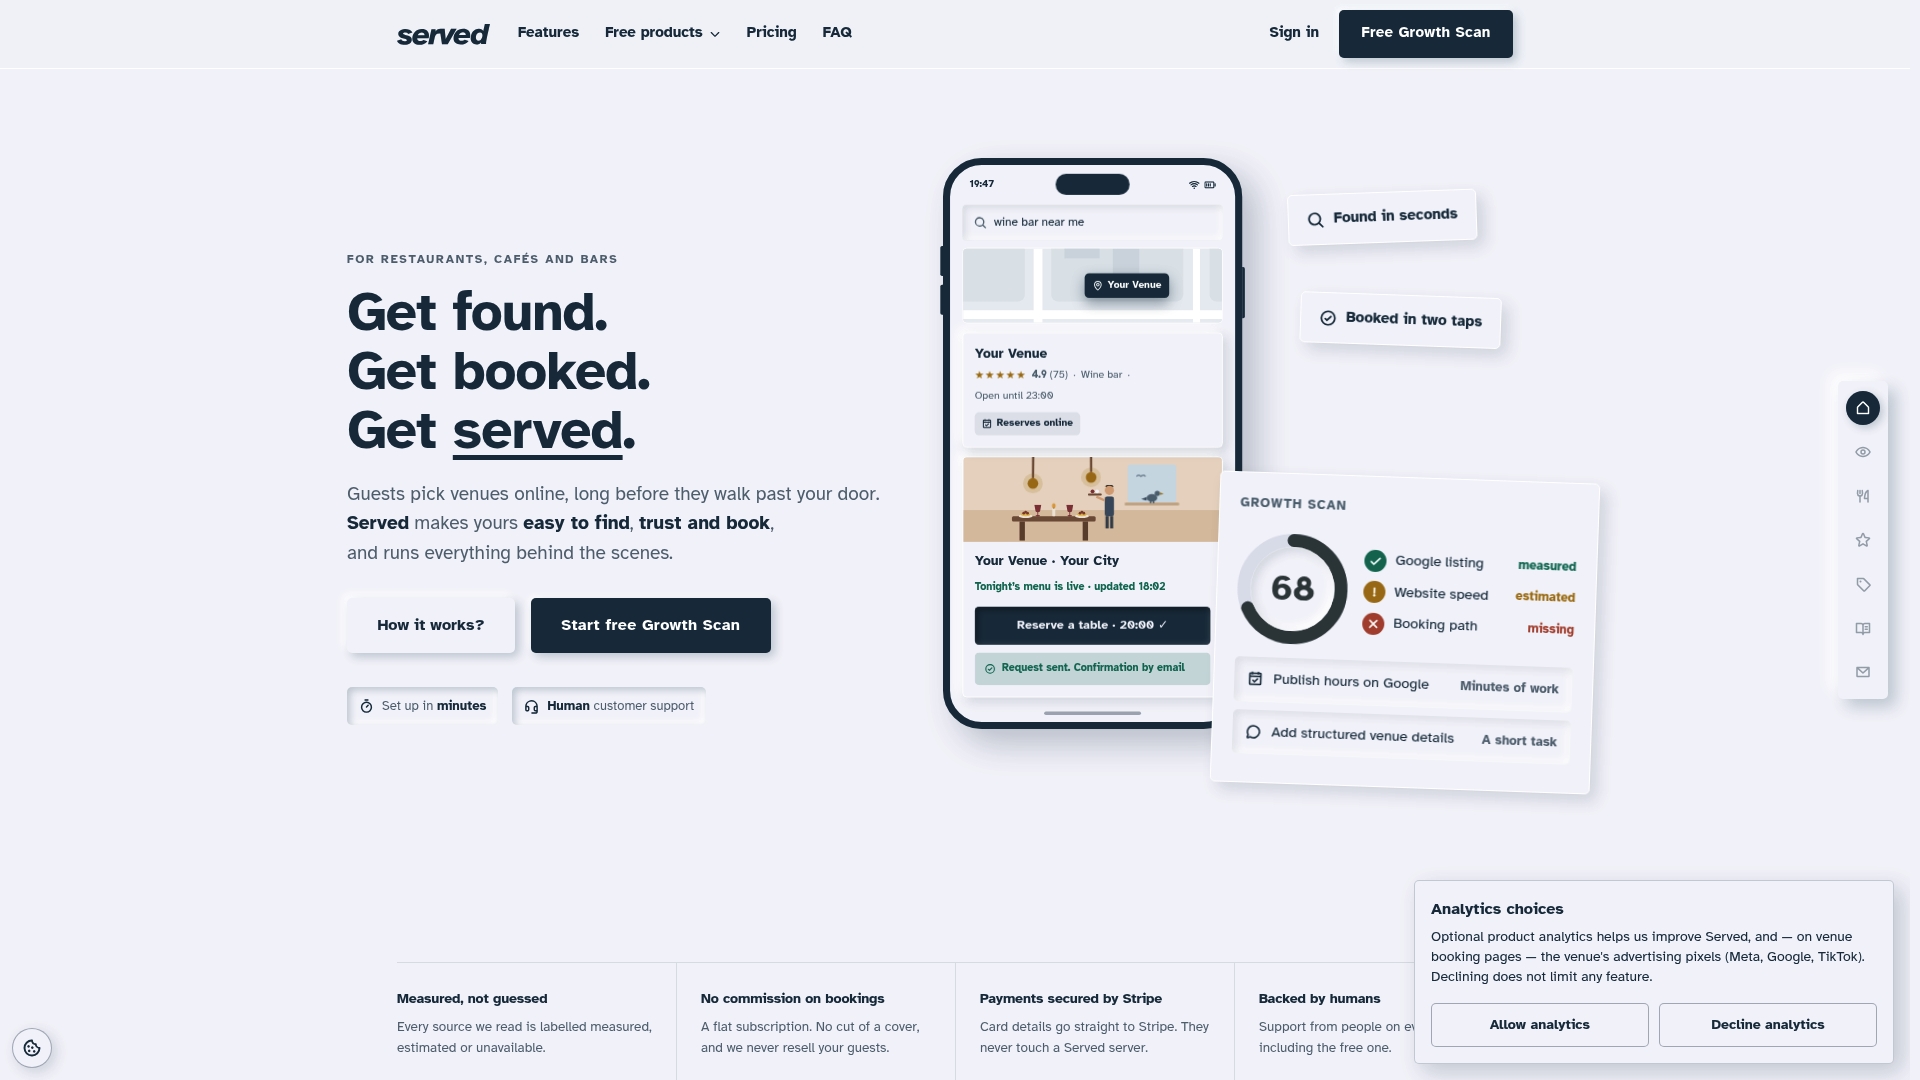
A Growth Scan shows venues exactly where their bookings currently come from and flags gaps in their visibility, and support from a person rather than a chatbot is included. If you want a quick, honest look at where your booking flow might be exposed, run a free Booking Path Scan or see how it all works on our page for hotels.
FAQ
How to track down someone who scammed you?
Start by reporting the transaction to your bank and the booking platform, both of which can trace account activity tied to the fraudulent listing. For US-based incidents, file a report with the FTC or through IC3, which centralise complaints for law enforcement investigation.
Can I get phished just by opening an email?
Opening a plain email is generally low risk, but clicking a link or downloading an attachment inside it is where the danger lies. Treat any unsolicited confirmation email, especially one you did not initiate, with caution before interacting with it.
How to prevent yourself from being scammed?
Pay only through the official booking platform, verify any unexpected request by calling the venue directly using a number from the confirmed listing, and never re-enter card details via a link in an unsolicited message. Keeping your confirmation PIN and transaction ID on hand also makes reconciliation faster if something looks wrong.
How do I check fraud on my name?
Review your bank and card statements for unfamiliar charges, and check whether any booking platforms you use show login activity you do not recognise. If you suspect your details have been used fraudulently, report it to your bank and file a complaint with a national reporting portal such as the FTC.
Sources
- Digital Services Act: notice-and-action mechanism
- Phishing attacks are using real hotel reservation info to target travelers
- BSI newsletter: phishing campaigns targeting travel bookings